CIS SecureSuite Product Vendor
 CIS SecureSuite Product Vendor
Know exactly which controls to implement first.
FrameworkMapper shows what your current tools already cover across CIS, CMMC, NIST, HIPAA and more. Then it ranks what to fix next by real-world threat impact, not guesswork.
970+ security tools mapped · 10 frameworks · 24 industries
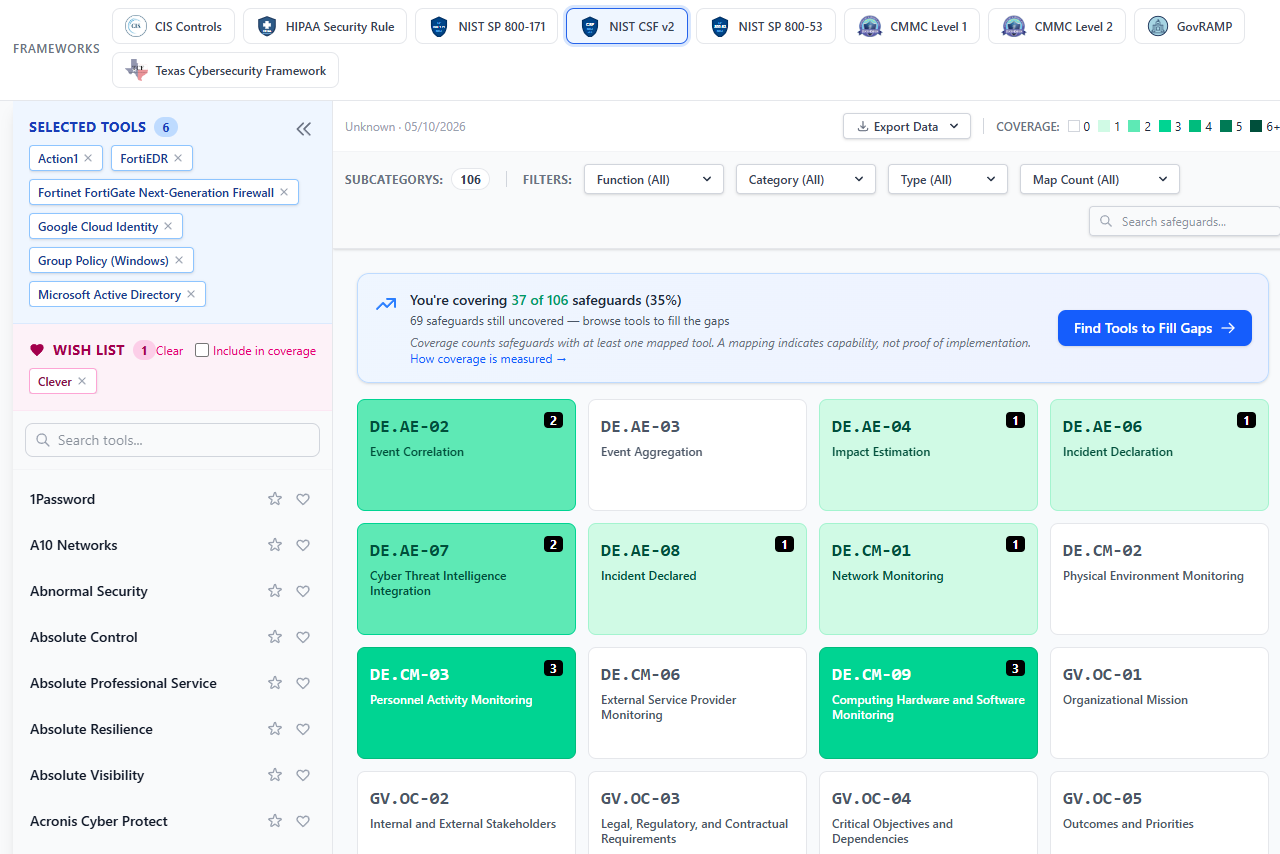
Frameworks FrameworkMapper maps
- CIS Controls
- CMMC Level 1
- CMMC Level 2
- NIST CSF v2
- NIST SP 800-53
- NIST SP 800-171
- HIPAA Security Rule
- GovRAMP
- CJIS
- Texas Cybersecurity Framework
Where are you starting from?
No security background required. Pick your path.
We need to get compliant
No dedicated security staff? See where you stand and what to fix first, in plain language.
Start freeWe run our own security program
Your team has the expertise. FrameworkMapper adds the structure: assessments, roadmaps, and maturity tracking over time.
See assessmentsI help local clients get compliant
Deliver branded assessments to every client and manage them all from one place.
Partner programWe manage security for many clients
One dashboard for your whole portfolio. Assessment credits on demand, no sales call to start.
Partner programHow it works
From “where do we start?” to a plan you can defend.
CIS IG1 safeguards alone block 77% of top attack types. Knowing which ones you’re missing is most of the battle.1
Map what you have.
List the security tools you already own. See which controls they cover across every framework, color-coded. Free with an account.
Fix what matters first.
Every gap is ranked by real threat impact, with specific tool recommendations and reports your leadership will actually read.
Prove it and be ready.
Run a guided assessment with a verifiable certificate. The same data builds your incident response plan, with no re-entry.
Then keep the score moving all year with progress check-ins, so next year’s assessment is a confirmation, not a surprise.
See the full program lifecycleAnswers you can defend to an auditor, a board, or a superintendent.
FrameworkMapper answers the three questions every security leader gets asked:
What do we fix first?
What should we buy?
What can an attacker still do to us?
Every answer comes from a published scoring method. Same inputs, same result, every time. No black-box AI deciding your priorities.
- CIS SecureSuite Product Vendor
- Published methodology
- Tool trust scored from public registries like CISA KEV, FedRAMP, and FIPS 140, never vendor self-attestation
Built for your industry.
Recommended frameworks and priorities tuned to 24 sectors.
K-12 Education
Safeguards prioritized for tight budgets and small IT teams.
Learn more →State Government
Framework compliance for agencies with federal grant requirements.
Learn more →Local Government
Practical compliance for municipalities, counties, and local agencies.
Learn more →Defense Industrial Base
A CMMC roadmap for DoD supply-chain contractors.
Learn more →Small Business
Essential cyber hygiene without a security team.
Learn more →Houses of Worship
Protect your congregation’s data with low-cost controls.
Learn more →Start free. Upgrade when you’re ready.
Explore the tools free with an account. A full year of assessments, incident response planning, and progress tracking starts at less than one week of a security analyst’s time, with pricing based on your frameworks and organization type. Complete a two-minute profile and your exact price appears in your dashboard. Partners get portfolio pricing with no sales call required.
Sources
- Center for Internet Security. CIS Community Defense Model v2.0. cisecurity.org